Osinto.ai - Collective Intelligence Exercise
‘Hybrid Security Threats, Europe’
Inside a dedicated instance of our Joint Tactical Operations Centre (JTOC), practitioners across Security, Resilience & Defence engage in a fictional hybrid campaign alongside their normal work, as it unfolds across a European port region throughout one week, with three new developments each day.
Participants bring their professional experience, leadership and solutions. Working with peers and published open-source reporting, they build a shared picture of the campaign, discuss courses of action and learn from each other’s assessments and decisions.
A fictional campaign. Open-source reporting. Shared intelligence in minutes.
The threat
European hybrid security threats involve coordinated, non-military or sub-threshold activities by state and non-state actors, principally Russia, Belarus and Iran, designed to destabilise European democracies and infrastructure.
The response
Threats rarely stay within one sector or one organisation's view. No single organisation sees the whole picture; each of us holds part of it. The JTOC brings practitioners together in one place, so fragmented open-source information becomes shared awareness and decision advantage.
A state-aligned campaign targets one North Sea port region over one week, hitting energy, transport and a defence manufacturer at once.
The port city of Ostrand is home to an LNG import terminal supplying about 15% of national winter gas, the rail freight operator that carries its cargo inland, and a manufacturer of air-defence components for European armed forces. It is late January. Gas prices are high, a cold spell is forecast, and there has been regional reporting of unexplained drone sightings near ports and energy sites. All names are fictional.
Days 1 to 3
The attack
Incidents arrive one after another across different domains: drone sightings, sabotage, a suspected cyber intrusion, disinformation and threats against people. The question is which of them are connected, and how sure you can be.
Days 4 and 5
The aftermath
The consequences play out: attribution under uncertainty, travel decisions, disruption to supply chains, and what to tell regulators, insurers and peers.
Share, Synthesise, Discuss
The scenario is fictional. The material is real. Each inject asks you to bring in published reporting, research and advisories on the same kind of threat, along with your own professional experience. The more participants share, the more the Intelligence Database can find, connect and synthesise. For each inject, contribute what you can. You do not need to do all three every time.
Share
Bring in a relevant published report, advisory or piece of research, with a short summary in your own words and its date. Attach documents in full, and add what your own experience tells you.
Synthesise
Put a specific question to everything already shared, using the Intelligence Database. Look for evidence, not verdicts.
Discuss
Challenge, qualify or apply the result to your own sites, staff, supply chains or travel.
Inside the exercise JTOC
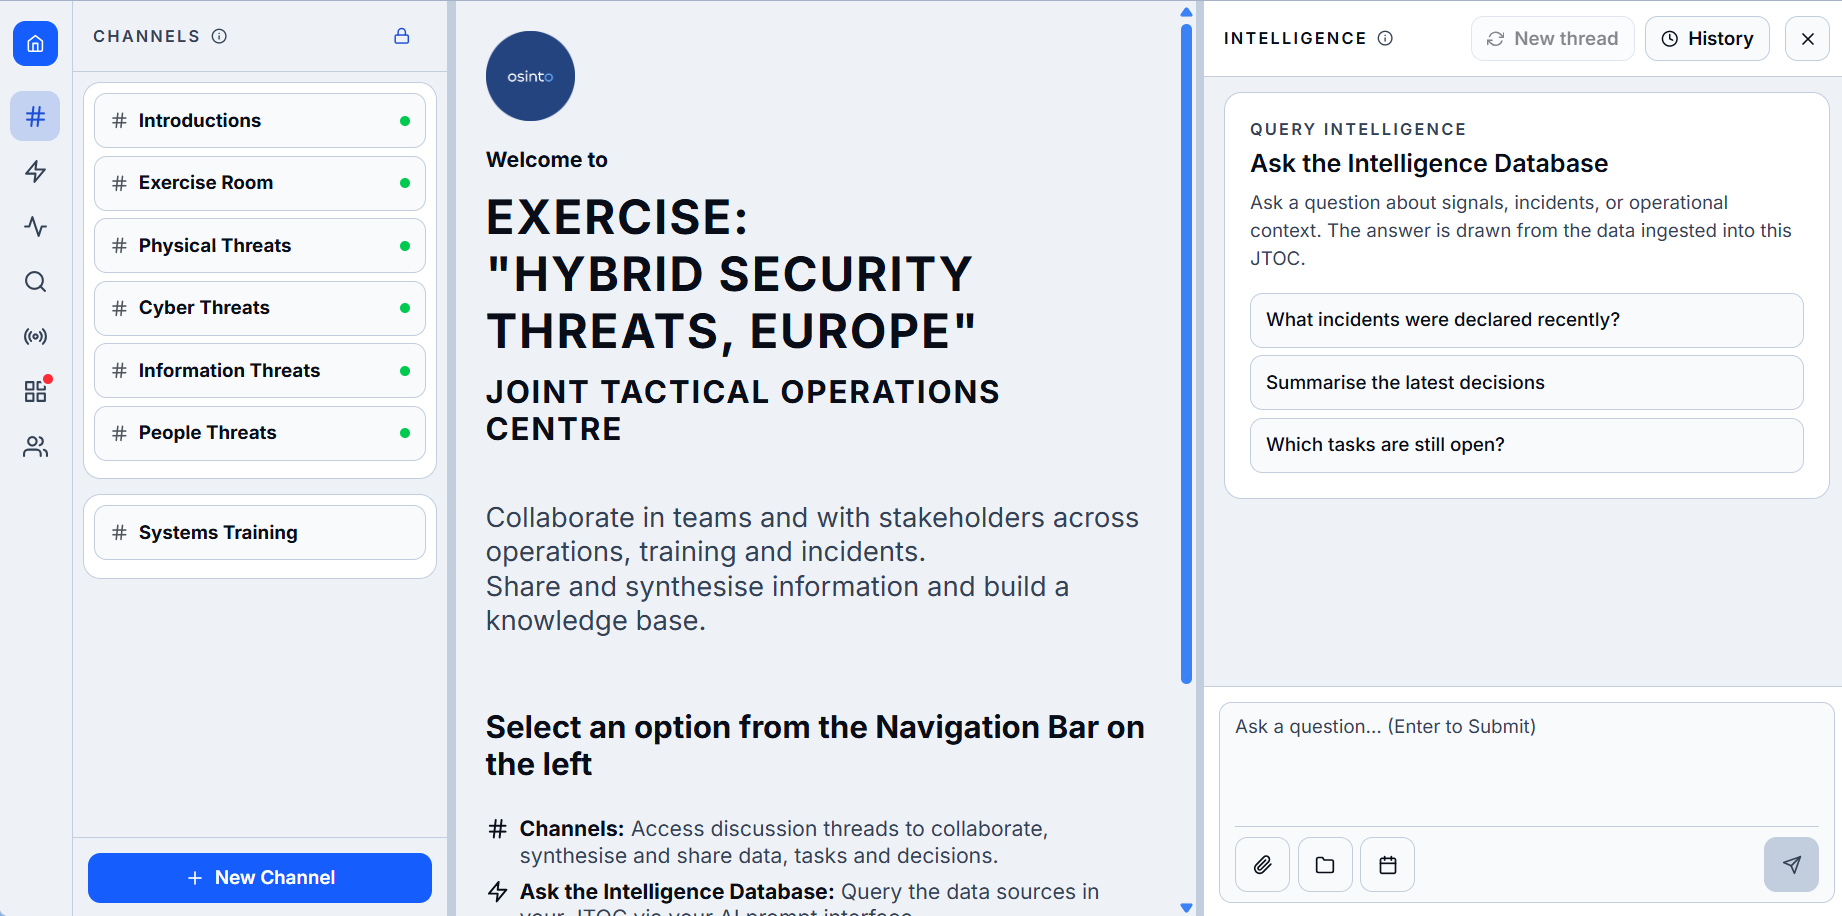
Injects arrive in the Exercise Room. Breakout discussion runs in the threat channels.
The Intelligence Database sits alongside, open to every participant.
Participants represent a cross-section of Security, Resilience & Defence and interested stakeholders.
Within the exercise, they share, synthesise, and discuss published open-source reporting, bringing their unique perspectives and solutions on subjects including sabotage, drone incursions, infrastructure disruption, cyber attacks, executive protection, disinformation, civil unrest, and border pressure—and their impact on sites, staff, supply chains, and travel.
Choose a perspective, not a role.
When you join, introduce yourself with one perspective. It is a lens, not a restriction, and nobody is assigned anything.
Places are limited. The exercise starts at 09:00 CET on Monday 2 November.
At a glance
Length
One working week, Monday to Friday. Days 1 to 3 are the attack; days 4 and 5 are the aftermath.
Injects
Three a day, at 09:00, 12:00 and 16:00 CET, all posted in the Exercise Room, each pointing to a breakout channel on its subject.
Flexible Engagement
Engage with each day’s developments as your time permits.
Decision points
Five injects ask for a short decision record. The rest are open discussion.
Intelligence Database
Open to every participant through their Intel feed for the week. Shared material becomes searchable, connected intelligence within minutes. Agentic functions are not available during the exercise.
Where
A dedicated JTOC: one Exercise Room for the injects, with the network's four threat channels for breakout discussion.
What you take away
By the end of the week, participants should be able to:
- 01
Connect the indicators
Recognise and test links across physical, cyber, information and supply-chain indicators, without assuming that correlation proves coordination.
- 02
Build a shared assessment
Turn fragmented open-source reporting into a sourced, dated shared assessment, including uncertainty and contradictory evidence.
- 03
Decide under uncertainty
Make and record proportionate decisions under uncertainty: who owns the decision, and what would cause it to be revisited.
- 04
Know the sharing boundaries
Identify information-sharing boundaries: what can be shared, with whom, at what confidence and with what caveats.
- 05
Decide faster, together
Draw on collective knowledge, and the synthesis built from it, to reach well-sourced decisions sooner than any one organisation could alone.
Ground rules
Open sources, Chatham House Rule
You may use what you learn in the exercise. Outside the JTOC, you should not reveal who said it or which organisation they are from. Everything posted is visible to all participants and indexed for the Intelligence Database.
Well-grounded uncertainty beats a confident answer.
- Public information only. Never upload classified, restricted, client-confidential or operationally sensitive material.
- No personal data about real people, including executives' addresses, families or movements, and no real employee identities.
- No exploitable technical detail: no credentials, vulnerabilities or exact security arrangements.
- Add a source note to everything you share, and label your own contributions as fact, allegation or professional judgement.
- Treat Intelligence Database answers as a starting point for human judgement, never a conclusion.
On completion, participants can request to continue to engage via the Hybrid Security Threats to European Organisations JTOC, with full access to Intelligence systems, including agentic capability.
Organisations can also create their own JTOCs at any time.
(Commercial terms apply).
To participate in the next Exercise, please submit your details before 1800hrs CET, Wed 28th October 2026.
Participation is by invitation only.
Places are limited. Request an invitation below.